Top all-time · #2634

Adam Caudill
Personal blog · adamcaudill.comsecurityprogramming
Adam Caudill's personal blog at adamcaudill.com covers security and programming. Since 2012, 29 different Hacker News readers have linked it 42 times, most often “Responsible Disclosure Is Wrong”. It is still writing: the last post was on 2026-02-07, and you can follow it by feed.
Too few sampled comments (15) to say how often HN recommends it.?
Why HN links it
HN readers link Adam Caudill's 2015 post arguing that "responsible disclosure" should be replaced by "coordinated disclosure". Other linked posts cover security research and reverse-engineering.
Summarised by Claude from a sample of 15 HN comments that link here. Each comment is marked recommending, critical or neutral (citing without judging); how this works.
Adam Caudill: Security Leader, Researcher, Developer, Writer, & Photographer
Most-linked posts?
- Responsible Disclosure Is Wrong3 people · 11 mentions · first linked 2016-04-13
- Looking for value in EV Certificates3 people · 3 mentions · first linked 2017-04-09
- Seamless Phishing2 people · 2 mentions · first linked 2016-05-22
- TLS: 64bit-Ish Serial Numbers and Mass Revocation2 people · 2 mentions · first linked 2019-03-11
- AMI-Bios Sourcecode and UEFI Signing Key leaked?2 people · 2 mentions · first linked 2013-04-05
- Snapchat: API & Security2 people · 2 mentions · first linked 2012-11-06
What Hacker News says?
> Seems like basic courteousy Read https://adamcaudill.com/2015/11/19/responsible-disclosure-is...
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “Security.txt”Submitted Bitcoin is a Cult as a story · 393 points
HN discussion> Intel is committed to the industry best practice of responsible disclosure of potential security issues No, the industry best practice is coordinated disclosure . The term "responsible disclosure" is a misnomer that we'd be far better off if we, as a society, stopped using it. https://adamcaudill.com/2015/11/19/responsible-disclosure-is...
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “Intel Responds to Security Research Findings”Submitted AMI-Bios Sourcecode and UEFI Signing Key leaked? as a story · 93 points
HN discussionMSI will absolutely refuse to disclose the firmware to his laptop so that he can make it so his replacement does not also brick itself The IBM PC, XT, and AT came with a physical copy of the complete source code for the BIOS , several hundred pages in a 3-ring binder. (You can get a digital copy of it here: https://archive.org/download/bitsavers_ibmpcat150ferenceMar8... ) IBM did this, despite the fact that they str…
Comment linking /2013/04/04/security-done-wrong-leaky-ftp-server/
on “No POST after rm -rf /”Submitted The Sinking Ship of E-Mail Security as a story · 36 points
HN discussionThank you for saying "coordinated disclosure" instead of the misnomer, "responsible disclosure". n.b. https://adamcaudill.com/2015/11/19/responsible-disclosure-is...
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “Disclosing vulnerabilities to protect users”Submitted TLS Certificates from the Top Million Sites as a story · 8 points
HN discussionSome commenters are decrying that this post fails to meet the bar for "responsible disclosure". Please stop using that phrase. "Responsible disclosure". It's wrong and harmful , and the person who coined it agrees with me: https://adamcaudill.com/2015/11/19/responsible-disclosure-is... You want "coordinated disclosure" instead. Netgear doesn't do coordinated disclosure. They do non-disclosure. In the absence of a co…
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “Netgear Signed TLS Cert Private Key Disclosure”Submitted Seamless Phishing as a story · 8 points
HN discussionThis is completely off-topic, but I'm curious. How does one go about "reverse engineering" a protocol like what Snapchat uses? Do you just listen in on the bits that the phone sends (say, with Wireshark) and kind of guess and poke at it to see what each part does? Edit: after some research (like reading TFRepo), I found some links mentioned that give some info in case anyone else is curious too. http://adamcaudill.c…
Comment linking /2012/06/16/snapchat-api-and-security/
on “Ask HN: Take down my reverse-engineered Snapchat lib because they asked?”Submitted When Hashing Isn't Hashing (Cryptography) as a story · 4 points
HN discussion> While it does not stop even the most basic active attackers You just admitted that it's useless! https://adamcaudill.com/2014/02/25/on-opportunistic-encrypti...
Comment linking /2014/02/25/on-opportunistic-encryption/
on “Show HN: A decentralized social network with end-to-end encryption”Submitted Seamless Phishing as a story · 4 points
HN discussionThe term "responsible disclosure" is actually a bad term to use, even if you support it: https://adamcaudill.com/2015/11/19/responsible-disclosure-is... TL;DR "coordinated disclosure" is preferred.
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “Security Update for Microsoft Malware Protection Engine”Submitted Ruby OpenSSL and GCM Nonce Reuse Bug as a story · 3 points
HN discussionAs much as I'm inclined to agree with this line of argument in this particular case, I do take issue with the term "responsible disclosure" for many of the reasons outlined here: https://adamcaudill.com/2015/11/19/responsible-disclosure-is...
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “FBI paid professional hackers one-time fee to crack San Bernardino iPhone”Submitted Threat Modeling for Applications as a story · 3 points
HN discussion> If this is most feasible, ok, though it smells like the opposite of responsible disclosure. Read: https://adamcaudill.com/2015/11/19/responsible-disclosure-is...
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “Pwned Certificates on the Fediverse”Submitted Responsible Disclosure Is Wrong as a story · 2 points
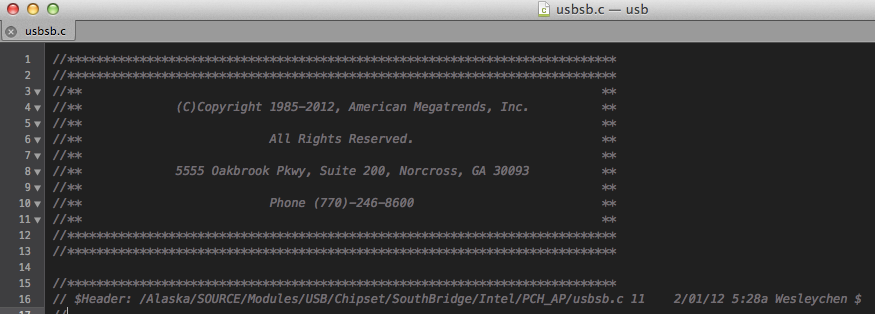
HN discussion>If the code was old, as it’s been when products like Symantec’s were leaked, this might not be so bad - but it’s not. > http://adamcaudill.com/files/Screenshot_4_4_13_10_04_PM.png >References in the files indicate that the code is from sometime in February - so this is current code. Given that that image shows dates in 2012, I think the author has made the classic mistake many of us make at the start of the new yea…
Comment linking /files/Screenshot_4_4_13_10_04_PM.png
on “AMI-Bios Sourcecode and UEFI Signing Key leaked?”Submitted Utilitarian Nightmare: Offensive Security Tools as a story · 2 points
HN discussion> If it's a security issue, then responsible disclosure. See: https://adamcaudill.com/2015/11/19/responsible-disclosure-is...
Comment linking /2015/11/19/responsible-disclosure-is-wrong/
on “Lavabit Security Misconfiguration”Submitted TLS: 64bit-Ish Serial Numbers and Mass Revocation as a story · 2 points
HN discussion> The good news is that Apple and Chrome did an amazing job at responding to this issue with the urgency that it deserves Excuse me? It is Google that assigned this as Chrome only. Over the last 7 days alone every single major Linux distribution has had to push an update (including Red Hat which assigned this a 9.6 score), and Docker images like Python which has over 1 billion pulls, not to mention Puppeteer(hello?)…
Comment linking /2023/09/14/whose-cve-is-it-anyway/
on “The WebP 0day”Submitted Confide, Screenshots, and Imaginary Threats as a story · 2 points
HN discussionScott Helme, a security researcher has an article on EV certificates and some of the issues with them in an article from December 2017 ( https://scotthelme.co.uk/are-ev-certificates-worth-the-paper... ). There was some discussion on this when it was originally submitted to HN at https://news.ycombinator.com/item?id=15850837 . Adam Caudill also has some insight here: https://adamcaudill.com/2017/04/09/looking-value-e…
Comment linking /2017/04/09/looking-value-ev-certificates/
on “Ask HN: Why most big websites aren't using EV SSL?”Submitted Looking for value in EV Certificates as a story · 2 points
HN discussionapi.snapchat.com is currently a CNAME to feelinsonice-hrd.appspot.com . Apparently the current API has been reverse-engineered very recently [1], with an alternate implementation publicly available [2]. Not good considering the nature of the app, perhaps there are some backwards-incompatible changes in the works? [1] http://adamcaudill.com/2012/12/31/revisiting-snapchat-api-an... [2] https://github.com/tlack/snaphax
Comment linking /2012/12/31/revisiting-snapchat-api-and-security/
on a deleted threadSubmitted On the need for an open Security Journal as a story · 2 points
HN discussion