Top all-time · #1121

Andrew Ayer
Personal blog · agwa.name/blog · on HN as agwasecuritywebsystems
Andrew Ayer's personal blog at agwa.name covers security, web and systems. Since 2013, 60 different Hacker News readers have linked it 110 times, most often “Git-crypt – transparent file encryption in Git”. It is still writing: the last post was on 2026-10-06, and you can follow it by feed.
Rarely recommended · 2 of 38 sampled comments recommend it?
Why HN links it
HN readers link Andrew Ayer's blog for write-ups on certificate authority incidents, TLS, and SSRF, and his git-crypt project page for keeping encrypted secrets in git repos.
- Recommended for · 2 comments
- One commenter calls its writeups on CA incidents and processes great; another calls a post on preventing SSRF in Go pretty good.
Summarised by Claude from a sample of 38 HN comments that link here. Each comment is marked recommending, critical or neutral (citing without judging); how this works.
Most-linked posts?
- Git-crypt – transparent file encryption in Git15 people · 20 mentions · first linked 2013-11-15
- Sign arbitrary data with your SSH keys5 people · 5 mentions · first linked 2021-11-12
- Duplicate Signature Key Selection Attack in Let's Encrypt4 people · 6 mentions · first linked 2015-12-02
- How to Crash Systemd in One Command4 people · 4 mentions · first linked 2016-09-28
- STARTTLS Considered Harmful4 people · 4 mentions · first linked 2014-08-13
- The SSL Certificate Issuer Field Is a Lie3 people · 7 mentions · first linked 2023-01-18
- Checking If a Certificate Is Revoked: How Hard Can It Be?3 people · 3 mentions · first linked 2022-12-01
- Preventing Server Side Request Forgery in Golang3 people · 3 mentions · first linked 2020-10-05
- Always Review Your Dependencies, AGPL Edition3 people · 3 mentions · first linked 2020-01-05
- /projects/git-crypt/2 people · 3 mentions · first linked 2013-02-06
What Hacker News says?
> UPDATE: Before people ask the potential question how the researchers are supposed to get their proper credit - my consideration is the following: Each of the researchers signs the paper with their own "public" key of a public-private key pair. This signature is uploaded as part of the paper upload. The "public" key is nevertheless kept secret by the researchers. > When the legal risk is over and the researchers wa…
Comment linking /blog/post/duplicate_signature_key_selection_attack_in_lets_encrypt
on “Intel Publishes Microcode Patches, No Benchmarking or Comparison Allowed”Submitted Sign arbitrary data with your SSH keys as a story · 637 points
HN discussionTo be clear, emSign is another name for EMudhra, and Comodo is now known as Sectigo. (You can't just look at the organization name in a certificate subject; you have to consult the CCADB: https://www.agwa.name/blog/post/the_certificate_issuer_field... )
Comment linking /blog/post/the_certificate_issuer_field_is_a_lie
on “eMudhra intermediate CA compromise”Submitted Google suspended my company's Google cloud account for the third time as a story · 416 points
HN discussionI use git-crypt to encrypt the inputs in my public repo https://www.agwa.name/projects/git-crypt/ :)
Comment linking /projects/git-crypt/
on “Advent of Code 2025”Submitted Always Review Your Dependencies, AGPL Edition as a story · 253 points
HN discussion100% agree. It's such a versatile tool -- for example I have the following: git config --local core.hooksPath $PWD/.githooks export DOCKER_CONFIG=$(realpath secrets/docker) Combine that with git-crypt[0] (obviously, don't commit secrets in plaintext to your repo!) for example and you have some really nice ergonomics. Not enough people know about direnv. [0]: https://www.agwa.name/projects/git-crypt/
Comment linking /projects/git-crypt/
on “New(ish) command line tools”Submitted How to Crash Systemd in One Command as a story · 224 points
HN discussionThese kinds of attacks are usually run by a major threat actor (i.e. nation state), targeted, and not run at large scale. Certificate transparency is unlikely to help in this case. Key pinning was the more secure option. For some issues see: https://www.agwa.name/blog/post/how_will_certificate_transpa... https://tools.ietf.org/html/draft-ietf-trans-threat-analysis...
Comment linking /blog/post/how_will_certificate_transparency_logs_be_audited_in_practice
on “Danish military intelligence uses XKEYSCORE to tap cables in co-op with the NSA”Submitted LibreSSL's PRNG is Unsafe on Linux as a story · 179 points
HN discussionYes it is, and they are awesome. git-crypt[0] is a godsend for smaller projects (and maybe larger ones if permissions are granular enough) -- way simpler than sops[1] and other alternative, with native integration via git filters (smudge). I use it on a ton of projects. [0]: https://www.agwa.name/projects/git-crypt/ [1]: https://github.com/mozilla/sops
Comment linking /projects/git-crypt/
on “Sign arbitrary data with your SSH keys”Submitted SQLite's documentation about its durability properties is unclear as a story · 145 points
HN discussionDirect link to the comment: https://bugzilla.mozilla.org/show_bug.cgi?id=1910322#c10 The author of that comment is Andrew Ayer, who also does great writeups about CA incidents and processes on his blog: https://www.agwa.name/blog/index
Comment linking /blog/index
on “DigiCert: Threat of legal action to stifle Bugzilla discourse”Submitted Using SNI proxying and IPv6 to share port 443 between webapps as a story · 138 points
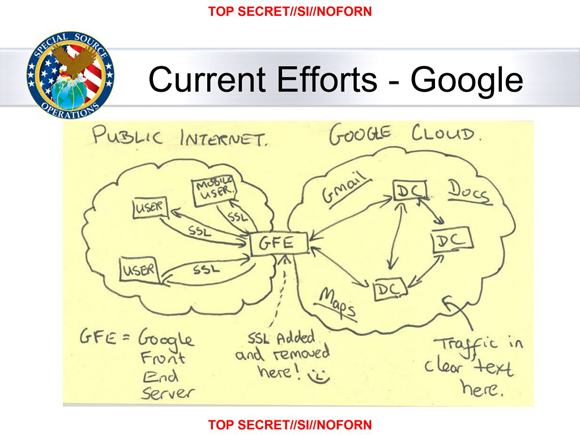
HN discussionNobody remembers the "SSL added and removed here :)"? https://www.agwa.name/blog/post/cloudflare_ssl_added_and_rem...
Comment linking /blog/post/cloudflare_ssl_added_and_removed_here/media/slide.jpg
on “Why is Cloudflare Pages' bandwidth unlimited?”Submitted Independently verifying Go's reproducible builds as a story · 137 points
HN discussionThese different representations also lead to frequent server side request forgery (SSRF) bypasses - someone might be blocking local IPv4 but you can still access their AWS metadata endpoint at ::ffff:169.254.169.254, etc. For anyone using Ruby, I'm the author of a gem [1] that comprehensively protects against SSRF bugs. For anyone using Golang I recommend this [2] blog post. [1]: https://github.com/arkadiyt/ssrf_fil…
Comment linking /blog/post/preventing_server_side_request_forgery_in_golang
on “Fun with IP address parsing”Submitted Git-crypt – transparent file encryption in Git as a story · 119 points
HN discussionI think that if you're using git, use git crypt[1][2] use git-dir and work-tree options/env vars [1] https://www.agwa.name/projects/git-crypt/ [2] though you have to remember to git crypt lock
Comment linking /projects/git-crypt/
on “One in every 600 websites has .git exposed”Submitted Thoughts on the Systemd Root Exploit as a story · 112 points
HN discussionLetsEncrypt was vulnerable to this exact attack - it let people issue valid TLS certificates for domains they didn't control: https://www.agwa.name/blog/post/duplicate_signature_key_sele...
Comment linking /blog/post/duplicate_signature_key_selection_attack_in_lets_encrypt
on “An Overview of Cryptography”Submitted Duplicate Signature Key Selection Attack in Let's Encrypt as a story · 71 points
HN discussionFor project-specific secrets, you may want to look at git-crypt: https://www.agwa.name/projects/git-crypt/
Comment linking /projects/git-crypt/
on “Sequoia-PGP – A new OpenPGP implementation in Rust”Submitted Comcast Shot Themselves in the Foot with MTA-STS as a story · 70 points
HN discussionSSL added and removed here! :-) https://www.agwa.name/blog/post/cloudflare_ssl_added_and_rem...
Comment linking /blog/post/cloudflare_ssl_added_and_removed_here
on “The NSA Selector”Submitted Systemd Is Not Magic Security Dust as a story · 59 points
HN discussiongit-crypt[1] is quite handy in cases where the credentials have to live along the code. It's a nice improvement over having credentials in clear in a git repo and relatively easy to implement. [1]: https://www.agwa.name/projects/git-crypt/
Comment linking /projects/git-crypt/
on “HashiCorp and Google: easing secret and infrastructure management”Submitted STARTTLS Considered Harmful as a story · 45 points
HN discussionAndrew Ayer has a write-up about this at https://www.agwa.name/blog/post/fixing_the_addtrust_root_exp... At the core, this is not a problem with the server, or the CA, but with the clients. However, servers have to deal with broken clients, so it’s easy to point at the server and say it was broken, or to point at the server and say it’s fixed, but that’s not quite the case. I discussed this some in https://twitter.c…
Comment linking /blog/post/fixing_the_addtrust_root_expiration
on “CA Root expired on 30 May 2020”Submitted Git-crypt – Transparent file encryption in git as a story · 29 points
HN discussion