Top all-time · #2828

Gamozo Labs Blog
Personal blog · gamozolabs.github.iosecuritysystems
Gamozo Labs Blog is a personal blog at gamozolabs.github.io about security and systems. Since 2018, 26 different Hacker News readers have linked it 37 times, most often “Vectorized Emulation: fuzzing at 2 trillion instructions per second”. The last post was in 2021, but the archive is still widely read.
I blog about random things security, everything is broken, nothing scales, shared memory models are flawed.
Most-linked posts?
- Vectorized Emulation: fuzzing at 2 trillion instructions per second9 people · 10 mentions · first linked 2018-10-15
- Sushi Roll: A CPU research kernel with minimal noise for microarch introspection8 people · 9 mentions · first linked 2019-08-19
- FuzzOS – an operating system which is designed specifically for fuzzing4 people · 4 mentions · first linked 2020-12-07
- Rust on MIPS64 Windows NT 4.02 people · 2 mentions · first linked 2021-11-16
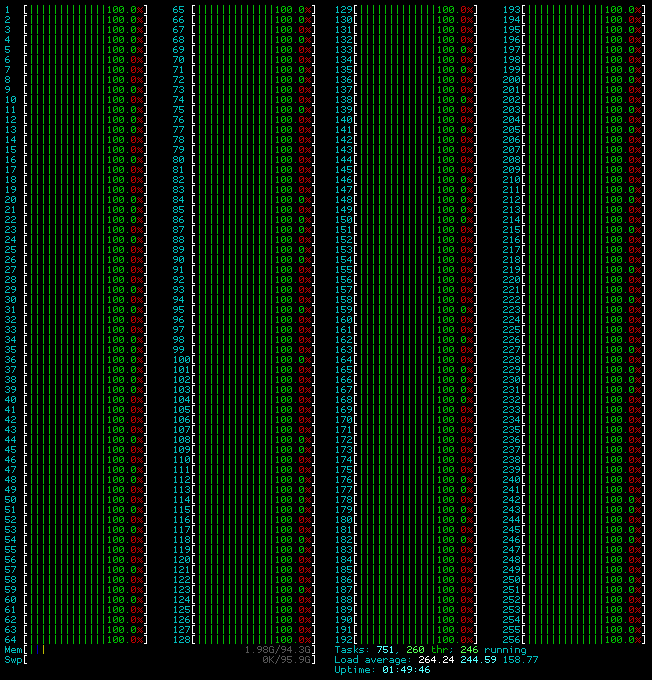
- Scaling AFL to a 256 thread machine2 people · 2 mentions · first linked 2018-09-17
- Finding 0day with the World's Worst Android Kernel Fuzzer2 people · 2 mentions · first linked 2018-10-20
What Hacker News says?
Nah, to be fair, the most compelling application is: https://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e...
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “AMD Zen 3/Ryzen 5000 announcement [video]”Submitted Rust on MIPS64 Windows NT 4.0 as a story · 203 points
HN discussionCoincidentally, this recent HN post also contains a fine introduction to processor internals of this sort: https://gamozolabs.github.io/metrology/2019/08/19/sushi_roll... . I know you (BeeOnRope) don't need the introductory parts, but you might appreciate the meat of his post.
Comment linking /metrology/2019/08/19/sushi_roll.html
on “Where do interrupts happen?”Submitted Vectorized Emulation: fuzzing at 2 trillion instructions per second as a story · 181 points
HN discussionSorry about that. This blog kinda just hopped into the meat of it as I was trying to keep it short. It's largely a followup to a previous blog of mine https://gamozolabs.github.io/metrology/2019/08/19/sushi_roll... where I go into the details and descriptions.
Comment linking /metrology/2019/08/19/sushi_roll.html
on “CPU Introspection: Intel Load Port Snooping”Submitted CPU Introspection: Intel Load Port Snooping as a story · 180 points
HN discussionA few years ago there were some articles on doing vectorized emulation using avx512. Not exactly as much parallelism as GPU but still a step in similar direction. https://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e...
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “Let’s build a high-performance fuzzer with GPUs”Submitted FuzzOS – an operating system which is designed specifically for fuzzing as a story · 122 points
HN discussionSomeone wrote a SIMD-fuzzer across AVX512. Its quite possible that someone figures out an x86 emulator on GPUs that fuzzes register values, similar to AVX512 fuzzing. https://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e... ------ Fuzzing is unique in that 99% of code probably traverses the same set of if-statements or branches. Whenever code significantly diverges (usually defined by Fuzzers as a significant…
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “Ryzen Threadripper Pro 3995WX Spotted”Submitted Sushi Roll: A CPU research kernel with minimal noise for microarch introspection as a story · 74 points
HN discussionMicrosoft has, or had, a similar technology they use internally, called TKO: https://www.microsoft.com/security/blog/2020/05/04/mitigatin... It's written in Rust and is based around a version of Bochs modified for deterministic execution. It's got time-travel debugging (with WinDbg), which works by replaying forward from the nearest snapshot to the point at which the user is asking to move backwards to. The primary…
Comment linking /fuzzing/2020/12/06/fuzzos.html
on “Debugging operating systems with time-traveling virtual machines (2005) [pdf]”- ot · 2019-08-20
Submitted Sushi Roll: A CPU kernel for cycle-by-cycle micro-architectural introspection as a story · 53 points
HN discussion I agree that there's too much focus on FP, but SIMD is not all about FP. Every new SIMD ISA extension has something interesting for integer. Here's an article about JITing x86 to AVX-512 to fuzz 16 VMs per thread: https://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e...
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “Linus Torvalds on AVX512”Submitted Scaling AFL to a 256 thread machine as a story · 25 points
HN discussionEven then -- https://gamozolabs.github.io/assets/afl_256thread.png Note that this CPU has 128 threads, so half of that picture. For my usual terminal size I might get 0-2 processes listed below that...
Comment linking /assets/afl_256thread.png
on “64 Core Threadripper 3990X CPU Review”Submitted Scaling AFL to a 256 thread machine as a story · 15 points
HN discussionAll true. No real disagreement and I'm often saying "it all depends.." myself. :-) In this case, there is also some vagueness around "random" (predictable to what subsystem when ). I still suspect @kortilla is one of today's lucky 10,000 ( https://xkcd.com/1053/ ) or just read/replied too quickly. :-) There is a lot written that indicates that the complexity of modern CPUs is ill-disseminated. But there is also wond…
Comment linking /metrology/2019/08/19/sushi_roll.html
on “How much slower is random access, really?”Submitted Rust on MIPS Windows NT 4.0 as a story · 14 points
HN discussionThis kernel is just kind of a playground for projects I have. Specifically there were a few from this past year or so. I used this kernel originally for my vectorized emulator, which is designed as a high-performance fuzzer/harness to find bugs (more info https://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e... ). I used vectorized emulation on Windows DHCP to find multiple RCEs (which were disclosed earlier…
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “Sushi Roll: A CPU research kernel with minimal noise for microarch introspection”Submitted Miniblog: How conditional branches work in Vectorized Emulation as a story · 4 points
HN discussionThose interested in this talk which is sort of a Hennesy & Patterson-based course on CPUs compressed down to 43 minutes might also find this "CPU measurement OS" SushiRoll interesting: https://gamozolabs.github.io/metrology/2019/08/19/sushi_roll...
Comment linking /metrology/2019/08/19/sushi_roll.html
on “What every programmer should know about how CPUs work – Matt Godbolt [video]”- ot · 2025-06-07
Submitted Sushi Roll: A CPU research kernel for micro-architectural introspection (2019) as a story · 3 points
HN discussion Makes me think of the amazing https://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e...
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “How We Implement 10x Faster Expression Evaluation with Vectorized Execution”Submitted A CPU research kernel for cycle-by-cycle micro-architectural introspection as a story · 3 points
HN discussionhttps://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e...
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “First 96-Core AMD Zen 4 Threadripper Tests Show Utter Domination over Intel”Submitted FuzzOS as a story · 3 points
HN discussionSeems to be the same concept as in https://gamozolabs.github.io/fuzzing/2018/10/14/vectorized_e... , cool!
Comment linking /fuzzing/2018/10/14/vectorized_emulation.html
on “Implementing a GPU's Programming Model on a CPU”Submitted Writing the worlds worst Android fuzzer, and then improving it as a story · 3 points
HN discussionSubmitted Finding 0day with the World's Worst Android Kernel Fuzzer as a story · 3 points
HN discussionSubmitted Vectorized Emulation: Hardware accelerated taint tracking as a story · 3 points
HN discussion
Linked by the same people?
- JJosh Barczakjoshbarczak.com
- P
 Performance Matterstravisdowns.github.io
- W
 Winsider Seminars & Solutions Inc.windows-internals.com
- T
 TrustInSofttrust-in-soft.com
- D
 Denis Bakhvaloveasyperf.net
- S
 Sebastian Sylvansebastiansylvan.com
- R
 RealTime Data Compressionfastcompression.blogspot.com
- K
 Krister Walfridssonkristerw.blogspot.com