Top all-time · #5442

Hack the Galaxy
Personal blog · johnjhacking.com/blogsecurity
Hack the Galaxy is a personal blog at johnjhacking.com about security. Since 2020, 14 different Hacker News readers have linked it 15 times, most often “Bad RegEx in NPM package with 12k weekly installs hiding for 4 years causes SSRF”. The last post was in 2023, but the archive is still widely read.
John is a senior offensive security consultant and a security researcher.
Most-linked posts?
- Bad RegEx in NPM package with 12k weekly installs hiding for 4 years causes SSRF3 people · 3 mentions · first linked 2020-11-23
- Abusing Signal Desktop Client for Fun and for Espionage3 people · 3 mentions · first linked 2023-01-23
- UNEP Breached, 100K+ Employee Records Accessed2 people · 2 mentions · first linked 2021-01-11
- Indian Government Breached, Massive Amount of Critical Vulnerabilities2 people · 2 mentions · first linked 2021-02-22
What Hacker News says?
John Jackson (johnjhacking) is not jacksonhhax, though they're both part of the same group. For context, John's a vet who's employed in the field. And beyond that, he's published other sound security research in the past, e.g. https://johnjhacking.com/blog/cve-2020-28360/ ( https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-2836... , which links https://github.com/frenchbread/private-ip ) As for the attribution…
Comment linking /blog/cve-2020-28360/
on “Indian Government Breached, Massive Amount of Critical Vulnerabilities”Submitted Indian Government Breached, Massive Amount of Critical Vulnerabilities as a story · 301 points
HN discussionwhoever is behind it I find it hard to blame them. As they write on their blog: >> Governments have an obligation to protect the private data of its employees and citizens. In addition, the exposure of proprietary government data can be used for great means of manipulation and for other destructive purposes. While the NCIIPC operates a Responsible Vulnerability Disclosure Program, the recklessness and avoidance of c…
Comment linking /blog/indian-government-breached-massive-amount-of-critical-vulnerabilities/
on “Indian Government Breached, Massive Amount of Critical Vulnerabilities”Submitted UNEP Breached, 100K+ Employee Records Accessed as a story · 3 points
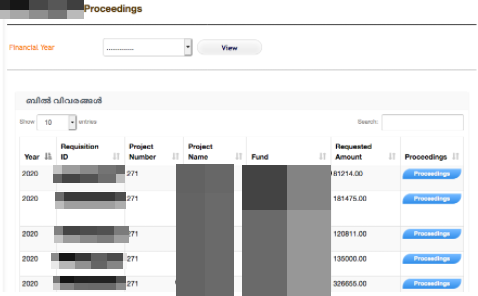
HN discussionEveryone seems to assume it is the central government. No one has remarked on this, the following somewhat obvious. One of the screenshots has a heading in Malayalam, saying "Bill Vivarangal" - "Bill details" [1]. Was it some government of Kerala service which was breached? Or is it one of several governments? Or was it only the central government with Malayalam as the language set for the interface? If it was an In…
Comment linking /uploads/session-chained.png
on “Indian Government Breached, Massive Amount of Critical Vulnerabilities”Submitted An Open Letter to the Japanese Government on Cybersecurity as a story · 2 points
HN discussionA friend of mine called in a pretty serious bug[0] post-Zoom acquisition and they jumped right on it, so they at least have clearance to handle security issues. [0] https://johnjhacking.com/blog/cve-2021-23827/
Comment linking /blog/cve-2021-23827/
on “Keybase.pub Shutting Down on March 1 2023”Submitted CVE-2022-27226: CSRF to RCE in iRZ Mobile Routers through 2022-03-16 as a story · 2 points
HN discussionSubmitted UNEP Breached, 100K+ Employee Records Accessed as a story · 2 points
HN discussionSubmitted Bad RegEx in NPM package with 12k weekly installs hiding for 4 years causes SSRF as a story · 2 points
HN discussionSubmitted Abusing Signal Desktop Client for Fun and for Espionage as a story · 1 points
HN discussionSubmitted Abusing Signal Desktop Client for Fun and for Espionage as a story · 1 points
HN discussionSubmitted Flaw in Signal Desktop ≤ 6.2.0 allows threat actor to obtain attachments as a story · 1 points
HN discussionSubmitted CVE-2020-28360: NPM private-IP SSRF Bypass (IP Phone Home) as a story · 1 points
HN discussionSubmitted PWK Gone Rogue (A PWN Story) as a story · 1 points
HN discussion