Top all-time · #8447
mrd0x.com
Personal blog · mrd0x.comsecurity
mrd0x.com is a personal blog at mrd0x.com about security. Since 2022, 9 different Hacker News readers have linked it 9 times, most often “Browser in the Browser (BITB) Attack”. No feed was found, so read it on the site itself.
Too few sampled comments (3) to say how often HN recommends it.?
Why HN links it
Linked for security posts, such as stealing tokens from Office applications, and for a distraction-free 'Sit' project. The comments cite or ask about it without judging the writing.
Summarised by Claude from a sample of 3 HN comments that link here. Each comment is marked recommending, critical or neutral (citing without judging); how this works.
Most-linked posts?
- Browser in the Browser (BITB) Attack4 people · 4 mentions · first linked 2022-03-15
What Hacker News says?
Interesting project. One thing I noticed: when I clicked the button, a fullscreen window got spawned, without any prompt asking me if I should enter fullscreen (Latest Firefox). On a sidenote: this could be used for browser-in-the-browser attacks[0] where someone could present a mock browser UI with a fake URL. Other than that, it's a great project. Anything to just sit without distractions gives us an unfair advant…
Comment linking /browser-in-the-browser-phishing-attack/
on “Sit.”Submitted Browser in the Browser (BITB) Attack as a story · 259 points
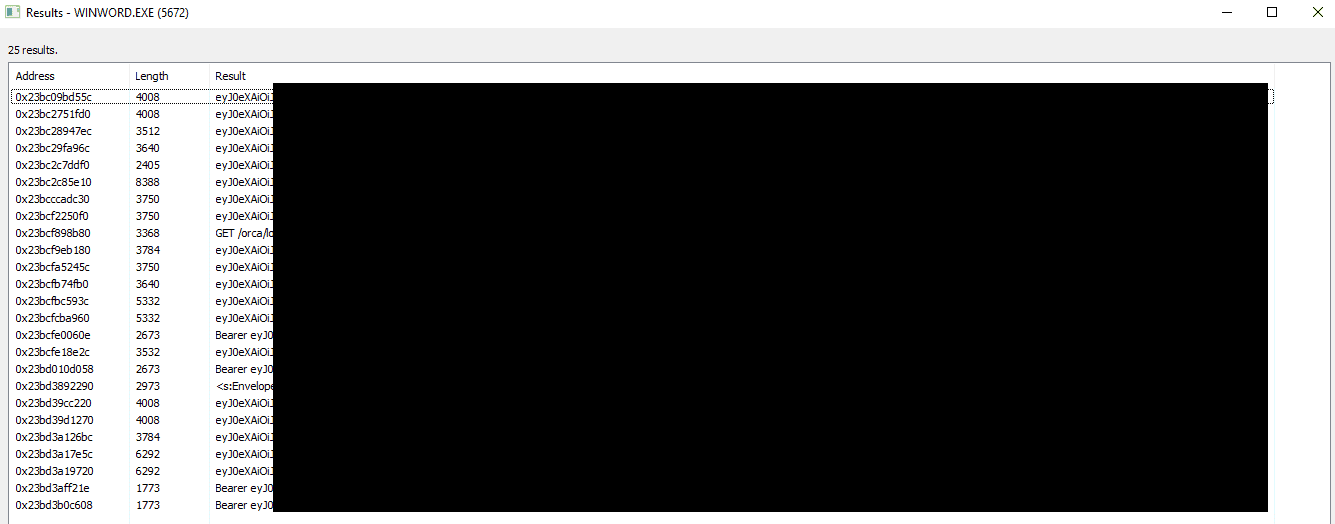
HN discussionAnyone know what that application is that's being used in that screenshot to search memory for strings? https://mrd0x.com/static/e0e177157e8596c60273e12d4b3bd695/4e...
Comment linking /static/e0e177157e8596c60273e12d4b3bd695/4e814/winword-tokens.png
on “Bringing Exchange Support to Thunderbird”Submitted Progressive Web Apps (PWAs) Phishing as a story · 132 points
HN discussionnobody supports 2fa on every mail request, that's just silly. Even MS's MFA is nothing more than a token that gets stored locally ( aka, a password ) and which can be stolen and be used elsewhere ( like a password! ) by hackers. https://mrd0x.com/stealing-tokens-from-office-applications/
Comment linking /stealing-tokens-from-office-applications/
on “Bringing Exchange Support to Thunderbird”Submitted Phishing with an in-browser remote desktop as a story · 53 points
HN discussionSubmitted Browser in the Browser (BITB) Attack as a story · 4 points
HN discussionSubmitted Browser in the Browser (BITB) Attack as a story · 3 points
HN discussionSubmitted FileFix – A ClickFix Alternative as a story · 1 points
HN discussion