Top all-time · #7437

NetSPI
Company blog · netspi.com/blogsecurity
NetSPI is the company blog at netspi.com, writing about security. Since 2013, 10 different Hacker News readers have linked it 12 times. It is still writing: the last post was on 2026-10-26, and you can follow it by feed.
Too few sampled comments (4) to say how often HN recommends it.?
Why HN links it
HN commenters cite NetSPI's security research, including a report testing Pixel-to-iPhone file sharing against OpenDrop, and a post on hardware attacks against secure enclaves. The comments cite the posts as sources and do not judge them.
Summarised by Claude from a sample of 4 HN comments that link here. Each comment is marked recommending, critical or neutral (citing without judging); how this works.
NetSPI is the proactive security solution used to discover, prioritize, and remediate security vulnerabilities of the highest importance. Schedule a demo.
Most-linked posts?
- /wp-content/uploads/2025/11/google-feature-review-report.pdf2 people · 2 mentions · first linked 2025-11-20
What Hacker News says?
I'm pretty sure this is just incorrect. According to the linked report[1], they tested it for compatibility with OpenDrop, so I think they simply implemented AWDL. That might also explain the limited Pixel 10 rollout, if it required a specific WiFi chipset/firmware. [1] https://www.netspi.com/wp-content/uploads/2025/11/google-fea...
Comment linking /wp-content/uploads/2025/11/google-feature-review-report.pdf
on “Android and iPhone users can now share files, starting with the Pixel 10”Submitted Stealing unencrypted SSH-agent keys from memory as a story · 81 points
HN discussionFrom the linked security report in that post https://www.netspi.com/wp-content/uploads/2025/11/google-fea... it seems like they implemented something similar to https://github.com/seemoo-lab/opendrop (which was also used to test interoperablity Also `we welcome the opportunity to work with Apple to enable “Contacts Only” mode in the future` doesn't make it sound like Apple actually helped implement this
Comment linking /wp-content/uploads/2025/11/google-feature-review-report.pdf
on “Android and iPhone users can now share files, starting with the Pixel 10”Submitted 1How to Bypass the PowerShell Execution Policy as a story · 4 points
HN discussionI was looking for the old CCC talk about this stuff, but I ended up finding out about a project called RayV Lite which seeks to democratize this hardware https://www.netspi.com/blog/executive-blog/hardware-and-embe... https://github.com/ProjectLOREM/RayVLite
Comment linking /blog/executive-blog/hardware-and-embedded-systems-penetration-testing/how-rayv-lite-is-democratizing-laser-fault-injection/
on “New attacks are diluting secure enclave defenses from Nvidia, AMD, and Intel”Submitted Cracking Stats for Q2 2014 as a story · 3 points
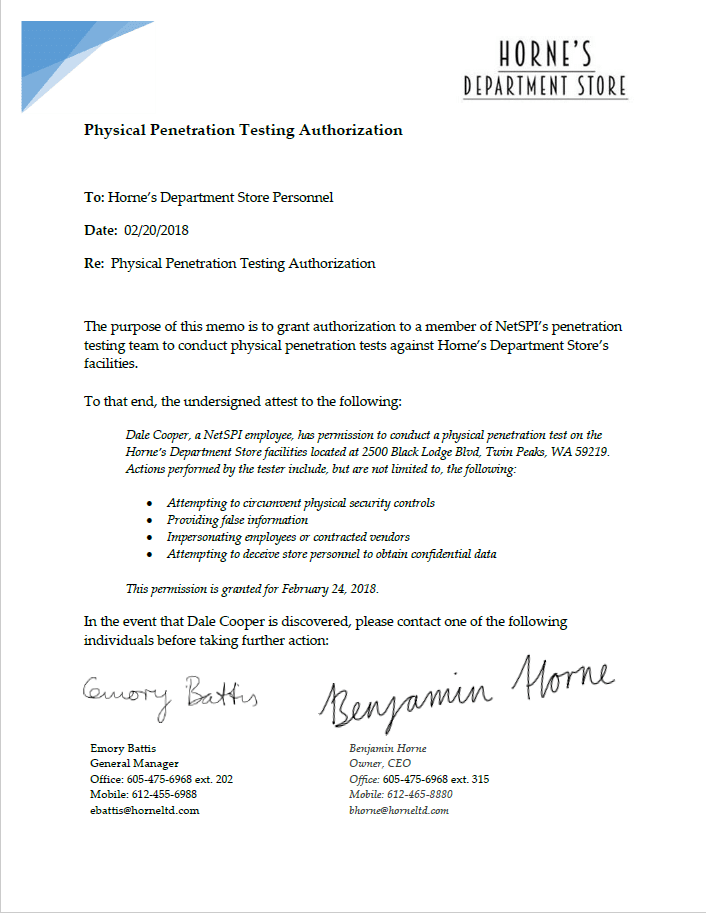
HN discussionI have done physical security red teams. It is 98% paperwork and planning that lets you do the 2% fun stuff. You carry a "get out of jail free card" (basic example below) which needs to be signed by someone high enough up to be able to authorize the work you are doing. I also request that it include contact info for at least 4 people who are aware of the testing and will answer their phone. Depending on the type of…
Comment linking /wp-content/uploads/2018/02/Physical-Penetration-Testing-Authorization-Sample.png
on “TSA Introducing Self-Service Screening Technology in Las Vegas”Submitted What Makes a Successful Technologist, a Day in the Life of a Security Firm CISO as a story · 2 points
HN discussionSubmitted Using Open Groups to Escalate Privileges in Google Cloud as a story · 1 points
HN discussionSubmitted Ethereum Virtual Machine Internals – Part 1 as a story · 1 points
HN discussionSubmitted GPU Password Cracking – Building a Better Methodology as a story · 1 points
HN discussionSubmitted Sky Prioritize Yourself as a story · 1 points
HN discussion