Top all-time · #2527

Volexity
Company blog · volexity.com/blogsecurity
Volexity is the company blog at volexity.com, writing about security. Since 2014, 30 different Hacker News readers have linked it 35 times, most often “A report on Chinese digital surveillance and hacking of Uyghurs”. It is still writing: the last post was on 2026-10-16, and you can follow it by feed.
Too few sampled comments (13) to say how often HN recommends it.?
Why HN links it
HN readers link Volexity's security write-ups on state-linked intrusions and zero-day exploitation, such as Confluence, Exchange, iOS Evil Eye and the Wi-Fi hop attack, mostly as primary sources.
Summarised by Claude from a sample of 13 HN comments that link here. Each comment is marked recommending, critical or neutral (citing without judging); how this works.
Volexity, the pioneer of memory forensics, delivers next-generation cybersecurity solutions - Volexity Volcano & Volexity Surge - and expert cyber threat intelligence & incident response services
Most-linked posts?
- A report on Chinese digital surveillance and hacking of Uyghurs4 people · 4 mentions · first linked 2019-09-03
- The Nearest Neighbor Attack4 people · 4 mentions · first linked 2024-11-22
- Zero-Day Exploitation of Atlassian Confluence3 people · 3 mentions · first linked 2022-06-02
- Dark Halo Leverages SolarWinds Compromise to Breach Organizations3 people · 3 mentions · first linked 2020-12-15
- Disgomoji Malware Used to Target Indian Government2 people · 2 mentions · first linked 2024-06-16
- StormBamboo Compromises ISP to Abuse Insecure Software Update Mechanisms2 people · 2 mentions · first linked 2024-08-05
- Active Exploitation of Multiple Zero-Day Microsoft Exchange Vulnerabilities2 people · 2 mentions · first linked 2021-03-02
What Hacker News says?
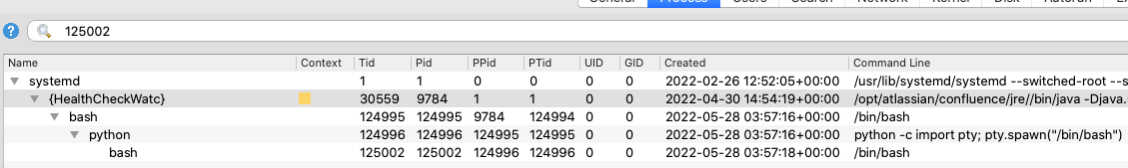
>No one sane runs confluence as root. See "Figure 1. Process tree in Volexity Volcano Server from the infected Confluence server" https://www.volexity.com/wp-content/uploads/2022/06/Figure1.... I didn't mean running as non-root would fix the problem, just that a remote root RCE was worse than a normal RCE.
Comment linking /wp-content/uploads/2022/06/Figure1.png
on “Zero-Day Exploitation of Atlassian Confluence”Submitted Zero-Day Exploitation of Atlassian Confluence as a story · 347 points
HN discussionWashington Post attributed the attack to Russian actor APT29/Cozy Bear on Dec 14th [1], quoting unnamed sources. FireEye [2] Dec 13th & Volexity [3] Dec 14th were more cautious, citing an unknown actor that they dubbed UNC2452, and Dark Halo, respectively. Recorded Future made a fair but ultimately inconclusive case for Chinese attribution [4], Dec 30th. US gov/CISA continues to claim "Russian linked" [5], Jan 5th.…
Comment linking /blog/2020/12/14/dark-halo-leverages-solarwinds-compromise-to-breach-organizations/
on “Solarwind, Fireeye, Microsoft and Cisco leaks are offered for sale”Submitted The Nearest Neighbor Attack as a story · 230 points
HN discussioniVerify uses a variety of methods to detect if the phone has a security issue. Some of them are deterministic and report with complete certainty. For example, the Volexity report about EVIL EYE includes IOCs for the exploit payload and we can detect and report whether that payload exists on your phone. (read that report here: https://www.volexity.com/blog/2020/04/21/evil-eye-threat-act... ) We also include more prob…
Comment linking /blog/2020/04/21/evil-eye-threat-actor-resurfaces-with-ios-exploit-and-updated-implant/
on “You’ve Got 0-Click Mail: Unassisted iOS Attacks RCE via Mobilemail/Maild”Submitted Multiple Russian Threat Actors Targeting Microsoft Device Code Authentication as a story · 186 points
HN discussionWe don't have precise information about the payload for the ZecOps bugs, so we can't say. The attacks profiled by Volexity earlier this week, the MobileSafari exploits that China was using to spy on Uyghurs, are now detected by iVerify. They released enough information that we pushed an update to all iVerify users to alert their phones if they were compromised. The Volexity report is here: https://www.volexity.com/b…
Comment linking /blog/2020/04/21/evil-eye-threat-actor-resurfaces-with-ios-exploit-and-updated-implant/
on “You’ve Got 0-Click Mail: Unassisted iOS Attacks RCE via Mobilemail/Maild”Submitted Palo Alto Networks PAN-OS Zero-Day Exploitation as a story · 95 points
HN discussionAn explanation of the attack by the company doing the investigation: https://www.volexity.com/blog/2024/11/22/the-nearest-neighbo...
Comment linking /blog/2024/11/22/the-nearest-neighbor-attack-how-a-russian-apt-weaponized-nearby-wi-fi-networks-for-covert-access/
on “Spies Jumped from One Network to Another via Wi-Fi in an Unprecedented Hack”Submitted A report on Chinese digital surveillance and hacking of Uyghurs as a story · 91 points
HN discussionMaybe so, but in this case they made it easy for them [1]: > Upon examining those logs, Volexity found that in January and February, password-spray attacks had been carried out against this service and three accounts had been successfully compromised by an attacker. > ... > The Enterprise Wi-Fi network, however, did not require MFA and only required a user's valid domain username and password to authenticate > ... >…
Comment linking /blog/2024/11/22/the-nearest-neighbor-attack-how-a-russian-apt-weaponized-nearby-wi-fi-networks-for-covert-access/
on “Spies Jumped from One Network to Another via Wi-Fi in an Unprecedented Hack”Submitted Pro-Democracy Websites in Hong Kong Targeted with and Serving Malware as a story · 61 points
HN discussionhttps://techcrunch.com/2019/08/31/china-google-iphone-uyghur... https://www.volexity.com/blog/2019/09/02/digital-crackdown-l... https://www.theguardian.com/world/2019/jul/27/the-world-know... https://www.forbes.com/sites/johnkoetsier/2019/09/06/apple-h...
Comment linking /blog/2019/09/02/digital-crackdown-large-scale-surveillance-and-exploitation-of-uyghurs/
on “Huawei Mate 30 phones launch without Google apps”Submitted Dark Halo Leverages SolarWinds Compromise to Breach Organizations as a story · 8 points
HN discussion> Interestingly, no one has done a deep dive on what Android exploits were hosted on the site that Google discovered Volexity did [1], although it's not clear if the android exploits were hosted on the same sites that google was referencing. [1]: https://www.volexity.com/blog/2019/09/02/digital-crackdown-l...
Comment linking /blog/2019/09/02/digital-crackdown-large-scale-surveillance-and-exploitation-of-uyghurs/
on “Exploit Market ‘Flooded’ with iOS Vulnerabilities”Submitted The Nearest Neighbor Attack: How a Russian Apt Weaponized Nearby Wi-Fi Networks as a story · 4 points
HN discussionThis was extensively covered when it first broke: https://news.ycombinator.com/item?id=31602288 https://www.volexity.com/blog/2022/06/02/zero-day-exploitati... (this article seems like blogspam to me)
Comment linking /blog/2022/06/02/zero-day-exploitation-of-atlassian-confluence/
on “Atlassian Confluence Server CVE-2022-26134 being actively expoited in the wild”Submitted Active Exploitation of Multiple Zero-Day Microsoft Exchange Vulnerabilities as a story · 4 points
HN discussionThe discoverers of the vulnerability posted this write-up: https://www.volexity.com/blog/2022/06/02/zero-day-exploitati... This looks like a bad one, folks. Their advice is "turn off your confluence server until a patch is available".
Comment linking /blog/2022/06/02/zero-day-exploitation-of-atlassian-confluence/
on “Confluence – Critical unauthenticated remote code execution vulnerability”Submitted StormBamboo Compromises ISP to Abuse Insecure Software Update Mechanisms as a story · 3 points
HN discussionhttps://www.volexity.com/blog/2021/05/27/suspected-apt29-ope... Many interesting details in this write-up from Volexity.
Comment linking /blog/2021/05/27/suspected-apt29-operation-launches-election-fraud-themed-phishing-campaigns/
on “Nobelium comprises USAID marketing service account, spoofs phishing emails”Submitted StormBamboo Compromises ISP to Abuse Insecure Software Update Mechanisms as a story · 3 points
HN discussionRelated: https://www.volexity.com/blog/2025/02/13/multiple-russian-th...
Comment linking /blog/2025/02/13/multiple-russian-threat-actors-targeting-microsoft-device-code-authentication/
on “Storm-2372 conducts device code phishing campaign”Submitted Newegg hacked, card information stolen for millions as a story · 3 points
HN discussionhttps://www.volexity.com/blog/2021/03/02/active-exploitation... https://www.reddit.com/r/sysadmin/comments/lwcnkn/exchange_s... https://www.reddit.com/r/sysadmin/comments/lwah3d/exchange_s... https://magoo.github.io/incident-tracking/2021/03/02/msft-ex... https://blogs.microsoft.com/on-the-issues/2021/03/02/new-nat...
Comment linking /blog/2021/03/02/active-exploitation-of-microsoft-exchange-zero-day-vulnerabilities/
on “Microsoft: Chinese Cyberspies Used 4 Exchange Server Flaws to Plunder Emails”Submitted Chained Exploitation of Ivanti Connect Secure Zero-Days as a story · 2 points
HN discussionSubmitted Disgomoji Malware Used to Target Indian Government as a story · 2 points
HN discussionSubmitted DriftingCloud: Zero-Day Sophos Firewall Exploitation and an Insidious Breach as a story · 2 points
HN discussionSubmitted Digital Crackdown: Large Scale Surveillance and Exploitation of Uyghurs as a story · 2 points
HN discussionSubmitted Russian hackers target NGOs with post-election phishing attacks as a story · 2 points
HN discussion