Top all-time · #861
cryto.net
Personal blog · cryto.net/~joepie91/blogprogrammingsecurity
cryto.net is a personal blog at cryto.net about programming and security. Since 2014, 78 different Hacker News readers have linked it 117 times, most often “Stop using JWT for sessions (2016)”. No feed was found, so read it on the site itself.
Sometimes recommended · 6 of 40 sampled comments recommend it?
Why HN links it
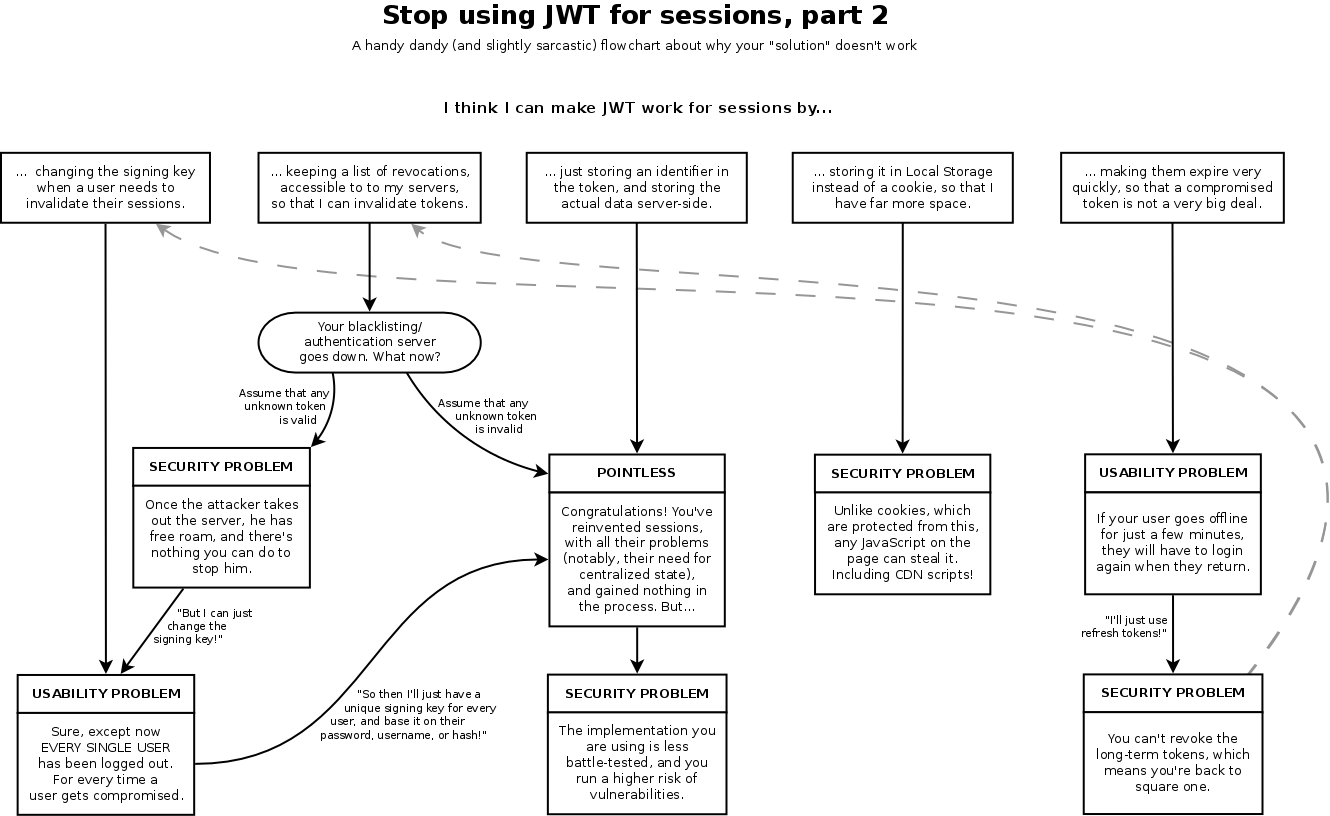
joepie91's blog, linked mainly for its argument against using JWTs for sessions, with a flowchart, and its criticism of MongoDB; often cited in JWT, auth and database discussions.
Summarised by Claude from a sample of 40 HN comments that link here. Each comment is marked recommending, critical or neutral (citing without judging); how this works.
Most-linked posts?
- Stop using JWT for sessions (2016)26 people · 27 mentions · first linked 2016-06-13
- Why not to use JWT, in 3 minutes21 people · 22 mentions · first linked 2016-06-18
- Never, ever, ever use MongoDB12 people · 14 mentions · first linked 2015-07-19
- Stop using JWT for sessions, part 2: Why your solution doesn't work (2016)9 people · 10 mentions · first linked 2016-06-19
- CloudFlare, We Have a Problem5 people · 7 mentions · first linked 2016-07-14
- A List of VPS Providers That Accept Bitcoin4 people · 4 mentions · first linked 2015-04-10
- Why Mt. Gox is full of shit3 people · 3 mentions · first linked 2014-02-10
- What is Promise.try, and why does it matter?2 people · 2 mentions · first linked 2016-05-11
- /~joepie91/blog/attachments/jwt-flowchart.png2 people · 2 mentions · first linked 2017-02-20
What Hacker News says?
This is probably a good moment to recall the article I published a while ago about how CloudFlare is actively putting the web at risk: http://cryto.net/~joepie91/blog/2016/07/14/cloudflare-we-hav... This is precisely why. The only thing that surprises me about this, is that it was an accidental disclosure rather than a breach. Other than that, this was completely to be expected . EDIT: Also, this can't be repeated e…
Comment linking /~joepie91/blog/2016/07/14/cloudflare-we-have-a-problem/
on “Cloudflare Reverse Proxies Are Dumping Uninitialized Memory”Submitted CloudFlare, We Have a Problem as a story · 297 points
HN discussion>MongoDB is like the Microsoft of operating systems. I'm not a Windows fan, but that's harsh. http://cryto.net/~joepie91/blog/2015/07/19/why-you-should-ne...
Comment linking /~joepie91/blog/2015/07/19/why-you-should-never-ever-ever-use-mongodb/
on “RethinkDB is shutting down”Submitted Why Mt. Gox is full of shit as a story · 277 points
HN discussionRather than just "JWT is awesome..." wouldn't it be more sensible and responsible to caveat this with some of the drawbacks? I read this article recently ( http://cryto.net/~joepie91/blog/2016/06/13/stop-using-jwt-fo... ) that proposes not to use it for sessions but instead for the use cases listed at the end of the article. Follow-up article here http://cryto.net/~joepie91/blog/2016/06/19/stop-using-jwt-fo... Also…
Comment linking /~joepie91/blog/2016/06/19/stop-using-jwt-for-sessions-part-2-why-your-solution-doesnt-work/
on “A practical security guide for web developers”Submitted Stop using JWT for sessions (2016) as a story · 248 points
HN discussionIt's a chicken egg problem. Developers use JWTs because it's what they think they know. Companies build libraries to support what developers are using. Security engineers say JWTs are easy to screw up [1]. Newer frameworks offer ways to move off of JWTs. New programming language comes out. New frameworks built for that programming language. What is someone most likely to build first as an integration? What developer…
Comment linking /~joepie91/blog/2016/06/19/stop-using-jwt-for-sessions-part-2-why-your-solution-doesnt-work/
on “Learnings from 5 years of tech startup code audits”Submitted Don't use JSON web tokens for sessions as a story · 226 points
HN discussionJWT is not a protocol but kind of a message format from my perspective. https://www.rfc-editor.org/rfc/rfc7519 It can be signed with HMAC SHA-256 algorithm: {"typ":"JWT", "alg":"HS256"} Ripping off JWT from surrounding context is a road to hell. It's worth to study JWT in context of OIDC (OpenID Connect) IDP providers. You will quickly bump into buzzwords like client (RP), server (OP), PKCE, Token Exchange, mTLS and…
Comment linking /~joepie91/blog/2016/06/19/stop-using-jwt-for-sessions-part-2-why-your-solution-doesnt-work/
on “Should I use JWTs for authentication tokens?”Submitted Never, ever, ever use MongoDB as a story · 182 points
HN discussionI don't like this one too much, because Mongo is wrong choice here domain wise, but this one was really convincing for me: http://cryto.net/~joepie91/blog/2015/07/19/why-you-should-ne...
Comment linking /~joepie91/blog/2015/07/19/why-you-should-never-ever-ever-use-mongodb/
on “PostgreSQL Scalability: Towards Millions TPS”Submitted The Day We Do Nothing Of Consequence as a story · 112 points
HN discussionWe’ve been going back and forth like this for quite a while, so at this point I doubt I’ll be able to convince you with further explanation. I’m shocked you think it’s “ivory tower nitpicking stated disingenuously” to call stateful tracking of nonces what it is - “stateful.” I’ll recuse myself from further “nitpicking” I suppose, because this isn’t going anywhere. If you’re interested in actually following why your…
Comment linking /%7Ejoepie91/blog/2016/06/19/stop-using-jwt-for-sessions-part-2-why-your-solution-doesnt-work/
on “Ask HN: What do you use for authentication and authorization?”Submitted Why you should never, ever, ever use MongoDB as a story · 98 points
HN discussionSomebody already addressed part of it, but here's an introductory guide to how licensing works: http://cryto.net/~joepie91/blog/2013/03/21/licensing-for-beg...
Comment linking /~joepie91/blog/2013/03/21/licensing-for-beginners/
on “The Daily Mail Stole My Visualization Twice”Submitted The Great Bitcasa Purge as a story · 50 points
HN discussionhttp://cryto.net/~joepie91/blog/2016/07/14/cloudflare-we-hav... If you're interested this guy has a really good response to exactly that question
Comment linking /~joepie91/blog/2016/07/14/cloudflare-we-have-a-problem/
on “Ask HN: Which companies have the best blogs written by their engineering team?”Submitted On Mozilla's forced SSL as a story · 46 points
HN discussionAnd, to be clear, using them for sessions is not one of those intended use cases, as joepie91 is arguing in that article. Using an actual server-side solution is easier and safer. For posterity, here's the second part to his crusade: http://cryto.net/~joepie91/blog/2016/06/19/stop-using-jwt-fo...
Comment linking /~joepie91/blog/2016/06/19/stop-using-jwt-for-sessions-part-2-why-your-solution-doesnt-work/
on “Don't Use VPN Services”Submitted CloudFlare, We Have a Problem as a story · 35 points
HN discussionThe author is a bit opinionated to say the least. He's also on a crusade against JSON web tokens and MongoDB. [0] http://cryto.net/~joepie91/blog/2016/06/13/stop-using-jwt-fo... [1] http://cryto.net/~joepie91/blog/2015/07/19/why-you-should-ne...
Comment linking /~joepie91/blog/2015/07/19/why-you-should-never-ever-ever-use-mongodb/
on “Don't Use VPN Services”Submitted Stop using JWT for sessions as a story · 20 points
HN discussionIndeed the article in question links here as required prior reading: http://cryto.net/~joepie91/blog/2016/06/13/stop-using-jwt-fo... So my comment was in the context of having read both of these. In the link here he also strongly argues against storage of JWT in localStorage.
Comment linking /~joepie91/blog/2016/06/13/stop-using-jwt-for-sessions/
on “JSON Web Tokens should be avoided”Submitted Reflections on NPM-gate, one day later as a story · 17 points
HN discussionJWT uses JWS, JWE, or both. Any criticism that targets JWE and JWS is necessarily relevant to JWT. The problems with JWT being addressed are in the domain of cryptography designs, so it's natural to criticize the cryptography components. The other problem with JWT is how people use it: http://cryto.net/~joepie91/blog/2016/06/13/stop-using-jwt-fo...
Comment linking /~joepie91/blog/2016/06/13/stop-using-jwt-for-sessions/
on “Things to Use Instead of JSON Web Tokens”Submitted Stop Using JWT for Sessions (2016) as a story · 15 points
HN discussionYou have to make your first payment via credit card so it's not anonymous unfortunately. joepie91 maintains a list, but it looks like it's a couple of years out of date: http://cryto.net/~joepie91/bitcoinvps.html
Comment linking /~joepie91/bitcoinvps.html
on “How Is NordVPN Unblocking Disney+?”Submitted Why not to use JWT, in 3 minutes as a story · 14 points
HN discussionToday I would still use alternatives like PASETO [0] or Branca [1] tokens which the latter is a fernet-like secure alternative to JWTs. The problem with JWTs is that they are discouraged by many cryptographers due to their "cryptographic agility" and provide a mixture of protocols which includes weak ciphers and configurations to shoot the programmer in the foot. Why include insecure ciphers in the first place? The…
Comment linking /~joepie91/blog/2016/06/19/stop-using-jwt-for-sessions-part-2-why-your-solution-doesnt-work/
on “Ask HN: What's the current sentiment on JWT for stateless auth tokens?”Submitted Stop Using JWT for Sessions as a story · 10 points
HN discussion